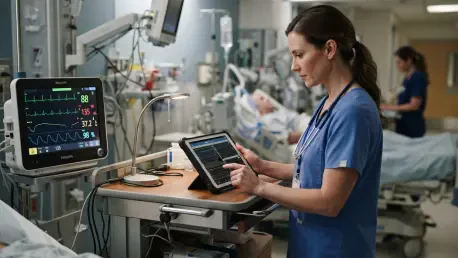
Integrating fusion gates into neural networks allows security systems to weigh temporal patterns against original traffic features for more precise attack classification. This technological shift arrives at a critical juncture for modern healthcare infrastructure, where the rapid proliferation of the Internet of Medical Things (IoMT) has fundamentally altered patient care by facilitating the real-time monitoring of vitals like heart rhythms and oxygen levels. However, this level of connectivity expands the attack surface for cyber adversaries significantly. Recent assessments indicate that nearly 99 percent of healthcare organizations manage devices with known security flaws, leaving over half of all medical equipment vulnerable to potential exploitation. In a clinical environment, a breach is far more than a financial disaster; compromised telemetry can lead to misdiagnosis or life-threatening treatment errors. Consequently, developing a robust, privacy-preserving intrusion detection system has become an essential priority for patient safety in the current landscape of 2026.
Decentralized Security and Advanced Neural Networks
Protecting Patient Privacy Through Local Training
Within a federated learning framework, the traditional paradigm of centralized data collection is discarded in favor of a localized approach where each medical device or gateway trains its own security model using private telemetry. Instead of transmitting raw, identifiable patient records to a central hub, only the resulting mathematical updates—referred to as weights—are shared. This structural change ensures that sensitive data remains within the hospital’s secure perimeter, mitigating the risks associated with a single point of failure or data theft on the black market. By keeping the raw information local, the system significantly reduces the volume of data traveling across the network, which prevents the congestion of hospital bandwidth during high-traffic periods. This method essentially allows the detection model to travel to the data, ensuring that the heavy lifting of machine learning occurs at the edge, where the information is generated and initially processed.
The decentralized nature of this architecture allows healthcare providers to maintain rigorous compliance with international data protection laws, such as HIPAA and GDPR, without sacrificing the benefits of advanced analytics. By aggregating weight updates from a vast array of sources, a central server can refine a global model that reflects a collective intelligence, which is then redistributed back to every participating device. This collaborative environment enables individual institutions to identify emerging threats that they might not have encountered locally, creating a unified defense against sophisticated cyberattacks. Furthermore, this approach fosters a culture of shared security without the legal and ethical hurdles of raw data exchange. As medical institutions integrate more diverse IoMT devices, this federated strategy provides a scalable way to enhance security protocols across entire healthcare networks, ensuring that even smaller clinics can benefit from high-level security insights.
Capturing Complex Attack Patterns With Hybrid Models
The structural core of this security framework relies on a hybrid deep learning architecture that integrates Recurrent Neural Networks (RNN) and Long Short-Term Memory (LSTM) layers to analyze network traffic sequences effectively. RNNs are particularly adept at identifying immediate anomalies, such as sudden spikes in packet transmission that often indicate the start of a flood-based denial-of-service attack. However, basic RNNs often struggle to maintain context over longer periods, which is where LSTM layers become indispensable. These layers utilize specific gates to retain or discard information, allowing the system to remember patterns across extensive timelines. This capability is vital for detecting “low-and-slow” attacks that are intentionally designed to unfold over several days to bypass traditional detection thresholds. By mastering both short-term fluctuations and long-term dependencies, the hybrid model provides a comprehensive shield that is far more effective than conventional signature-based security systems.
To further refine the accuracy of these hybrid models, researchers have implemented learnable fusion gates that dynamically balance temporal representations with original normalized traffic features. This mechanism allows the system to evaluate a network packet not just as an isolated event, but as part of a broader historical context, leading to a more nuanced understanding of traffic behavior. For instance, a slight change in header length might appear benign on its own, but when weighted against previous patterns of reconnaissance, it could be flagged as a precursor to a data injection attempt. This sophisticated weighing process reduces the likelihood of false positives, which are a major source of fatigue for hospital IT staff. By ensuring that every detection is grounded in a multifaceted analysis of the traffic stream, the fusion gate technology allows the security framework to differentiate between legitimate surges in medical data and malicious activities designed to mimic normal clinical operations.
Validation and Practical Implementation in Clinical Settings
Enhancing Efficiency With Bayesian Methods
Training sophisticated neural networks typically requires massive computational resources, often involving banks of high-end GPUs that are simply not feasible for most clinical settings to maintain. To address this bottleneck, researchers have turned to Bayesian optimization as a means of fine-tuning the security model’s parameters without the need for exhaustive, power-hungry searches. Traditional methods like grid search can take over a hundred hours to identify the optimal configuration for a model, a delay that is unacceptable when new cyber threats are constantly evolving. Bayesian optimization works by building a probabilistic map of the performance landscape, allowing the system to intelligently predict which settings will yield the best results. This allows the framework to converge on an ideal configuration in a fraction of the time, ensuring that the security system can be updated rapidly as new attack vectors are discovered, minimizing hardware demands.
Practical applications of Bayesian methods have demonstrated that it is possible to achieve near-perfect detection accuracy while utilizing approximately 30 times less compute power than conventional optimization techniques. In real-world trials, this approach reduced the training window from over a hundred hours to just a few hours, a breakthrough that enables more frequent and iterative updates to the global model. This efficiency is critical for maintaining a “living” security system that can adapt to the changing tactics of cybercriminals without disrupting the primary medical functions of the hospital. By lowering the barrier to entry for high-level AI security, Bayesian optimization ensures that even resource-constrained healthcare environments can deploy cutting-edge protection. The ability to refine security protocols seamlessly in the background means that clinical workflows remain uninterrupted, allowing doctors and nurses to focus on patient care with the confidence of robust digital protection.
Bridging the Gap With Explainable AI
A significant barrier to the adoption of artificial intelligence in healthcare is the “black box” nature of deep learning, where complex models provide a security alert without explaining the reasoning behind it. This lack of transparency can be problematic in a hospital setting, where an unexplained alert might lead to the unnecessary isolation of a life-saving device. To solve this, the framework integrates Shapley Additive Explanations (SHAP), a method that deconstructs every prediction to show which specific features contributed most to the final decision. By providing a clear ranking of factors, such as packet header length or flow duration, SHAP allows security analysts to understand exactly why a particular traffic flow was flagged as suspicious. This interpretability transforms the AI from an opaque decision-maker into a collaborative tool that provides actionable insights to human operators, bridging the gap between automated detection and informed clinical responses.
The practical utility of explainable AI became evident when distinguishing between a cybersecurity event and a genuine medical emergency. For instance, if an alarm was triggered, SHAP analysis revealed whether the anomaly was caused by network-level features, suggesting an attack, or by physiological features like heart rate variability, which indicated a change in the patient’s condition. This level of detail allowed hospital staff to prioritize their actions correctly, whether that involved calling a rapid response team or initiating a network lockout to contain a breach. By providing this vital context, the framework ensured that automated security supported clinical workflows rather than creating confusion. Furthermore, this transparency assisted in meeting international standards for auditable AI, ensuring that every security decision was reviewed and understood by regulatory bodies. Ultimately, the integration of these technologies solidified the defense of medical infrastructure for the long term.