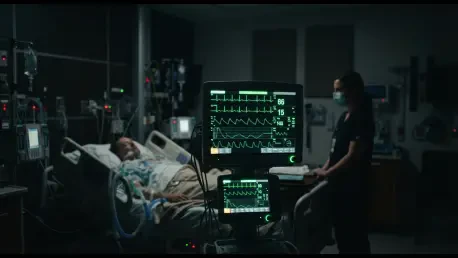
Regulatory enforcement bodies are now utilizing advanced analytics and AI tools to detect anomalies in data access and conduct more sophisticated audits of providers. This shift reflects a broader transformation where personal health information has transitioned from a backend administrative detail to a critical frontline strategic asset. In the current landscape, medical records contain far more than just treatment histories; they house sensitive financial data and genetic blueprints that make them high-value targets for cybercriminals. Recent data indicates that healthcare remains the most frequently targeted sector for ransomware attacks, marking a dangerous trend where data loss directly translates into care disruption. When hospital systems are paralyzed by encryption, the impact is measured in minutes lost for emergency responses and surgical delays. This reality has elevated data governance to a primary component of patient safety, forcing leaders to view cybersecurity as a clinical necessity.
Strengthening Operational Resilience and Regulatory Compliance
Transitioning from a reactive posture to a model of proactive operational preparedness has become the new standard for modern health systems. Compliance is no longer defined by the mere existence of a policy manual sitting on a shelf; instead, regulators require tangible proof that organizations can withstand a sustained cyberattack. This involves the implementation of rigorous network segmentation, which creates digital firewalls between different departments to prevent a breach in the billing department from migrating into the critical care units. Furthermore, the use of frequent tabletop simulations allows administrative and clinical teams to practice their response to a hypothetical ransomware event in a controlled environment. These exercises expose vulnerabilities in communication and technical recovery that might otherwise go unnoticed. The ability to detect an intruder within the network early is now viewed as the benchmark of institutional maturity and resilience.
The extensive network of third-party vendors that supports the healthcare ecosystem introduces a significant accountability gap that many organizations struggle to bridge effectively. While hospitals often outsource complex functions like data storage or telehealth platforms to specialized providers, the legal and ethical responsibility for patient privacy remains firmly with the primary healthcare organization. It is a common misconception that signing a contract transfers the risk to the vendor; in reality, a security failure at a partner organization is legally treated as a failure of the hospital itself. Consequently, due diligence must evolve from a one-time screening during procurement into a continuous, iterative monitoring process. This requires ongoing audits of vendor security protocols and regular updates to business associate agreements to reflect current threats. Ensuring that partners adhere to high security standards is essential for maintaining trust and patient safety.
Governing Artificial Intelligence and Proactive System Design
As healthcare facilities integrate artificial intelligence into their diagnostic and operational workflows, the governance of the underlying data requires a new level of scrutiny and transparency. AI systems are notoriously data-hungry, requiring vast repositories of patient information to train algorithms and generate accurate predictions. However, the practice of feeding every available data point into a machine learning model without a clear justification is no longer acceptable under modern privacy frameworks. Organizations are now mandated to implement “purpose of use” protocols, which ensure that only the minimum necessary data is utilized for a specific, documented medical or administrative goal. Furthermore, the drive toward explainable AI means that governance teams must be able to describe how an algorithm arrived at a specific clinical recommendation. This transparency is crucial for maintaining ethical standards and preventing bias in automated patient outcomes.
Building on these technological advancements, the industry is increasingly adopting a “Privacy by Design” framework to ensure that security is an inherent feature of every new service. This approach involves embedding technical controls and privacy safeguards into the initial architecture of a system rather than attempting to retrofit them after a breach has occurred. Such a strategy is particularly vital as integrated healthcare platforms become the norm, allowing medical records to flow seamlessly between primary care physicians, specialists, and laboratories. While this mobility significantly improves the coordination of patient care, it also creates expanded attack surfaces that are difficult to manage through traditional means. By incorporating real-time monitoring and enhanced visibility into these integrated systems, organizations can track every instance of data access as it happens. This proactive stance ensures that the convenience of digital health does not create massive security gaps.
Managing Internal Risks and Sophisticated Auditing Trends
Despite the focus on external hackers, the human element remains a persistent and complex vulnerability within the healthcare security landscape. A significant portion of unauthorized data access incidents originates internally, often stemming from unintentional errors, such as falling for a phishing email or misconfiguring a cloud database. To mitigate these risks, organizations must move beyond generic, annual training sessions and toward continuous, role-specific education programs that address the specific tools employees use daily. Fostering a corporate culture that prioritizes data hygiene as a core value helps ensure that staff members at all levels understand their role in protecting patient information. This includes teaching medical personnel how to recognize social engineering tactics and emphasizing the importance of strict access-permission discipline. When every employee views themselves as a guardian of patient privacy, the risk of exposure is significantly reduced.
The evolving landscape of healthcare security demanded a shift toward more sophisticated monitoring and a deep commitment to systemic resilience. To navigate this era successfully, healthcare leaders took decisive action by implementing advanced automated detection tools that mirrored the capabilities of regulatory auditors. They prioritized the consolidation of fragmented security protocols into a unified governance framework that addressed both clinical and administrative data needs. Furthermore, the industry moved toward a more collaborative model of threat intelligence sharing, where institutions pooled their knowledge to defend against common adversaries. By investing in continuous workforce development and prioritizing the ethical use of artificial intelligence, organizations ensured they remained ahead of both criminals and regulators. These steps represented a fundamental reinvestment in the trust that patients placed in their medical providers, ensuring safe care.