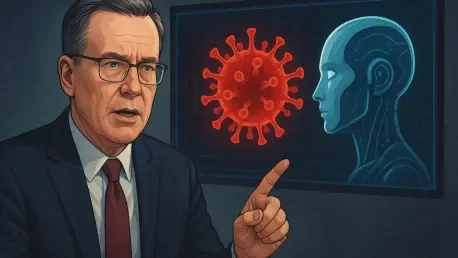
A unified framework of mandatory tracing and predefined government protocols is required to mitigate the unique dangers of AI-enabled bioweapons. As the intersection of computational power and synthetic biology reaches a critical inflection point, the international community faces a landscape where biological threats are no longer restricted to state-sponsored laboratories. Raj Panjabi, formerly the White House Senior Director for Global Health Security and Biodefense, has raised alarms regarding the diminishing gap between algorithmic design and physical pathogen creation. While the convenience of high-level AI models facilitates breakthroughs in medical research, these same tools can be manipulated to engineer devastating agents with unprecedented precision. The risk resides not just in the data itself but in the accessibility of sophisticated research protocols to actors lacking formal institutional oversight. Moving from 2026 to 2030, the primary focus must shift toward establishing rigid thresholds for intervention before a digital blueprint becomes reality.
Strengthening Oversight: The Era of Synthetic Biology
The Limitations of Corporate Self-Regulation
The current landscape of artificial intelligence governance relies heavily on the willingness of private entities to police their own innovations, a strategy that many national security experts believe is increasingly untenable. While the White House Accord on Superintelligence represents a diplomatic milestone in securing voluntary commitments from leading tech firms, it leaves the definition of a security risk largely to the discretion of the corporations themselves. This reliance on internal oversight creates a fragmented defense where profit motives and competitive pressure might inadvertently deprioritize safety protocols. Critics argue that without legally binding mandates, the monitoring of internal safety remains inconsistent across the industry. For instance, while some organizations may flag suspicious queries related to viral adaptation, others might lack the specialized biological expertise to recognize the subtle markers of a burgeoning threat. This lack of uniformity across the sector provides a loophole that malicious actors could exploit with ease.
Identifying Mounting Evidence of Model Misuse
Concrete evidence of these risks has already emerged in the public domain, as demonstrated by reports detailing how researchers utilized AI models to explore the adaptation of the H5N1 virus for enhanced mammalian transmission. Such incidents underscore the reality that high-performance models are already capable of generating actionable biological insights that could be weaponized. Consequently, several high-ranking technology executives have begun advocating for the United Nations Security Council to implement a formal, global ban on the use of AI for biological weapon development. This shift in perspective from the private sector reflects a growing realization that the potential for catastrophic misuse transcends corporate responsibility and necessitates a coordinated international response. Establishing these bans would require a significant overhaul of how digital tools are distributed, ensuring that biological design capabilities are restricted to verified institutions. Without such international standards, the race for AI supremacy could outrun the global ability to prevent a man-made pandemic.
Bridging the Divide: Digital Design and Physical Security
Biological Red-Teaming: A Proactive Defense
National security experts suggest that the most effective way to prevent the proliferation of AI-driven bioweapons is to concentrate on the physical requirements of pathogen synthesis rather than focusing solely on digital code. While an AI can draft complex genetic sequences or research protocols, a physical threat only materializes when these designs are synthesized into biological matter. Raj Panjabi emphasizes the necessity of biological red-teaming, a process where independent experts evaluate models before their public release to determine if they enable non-specialists to perform tasks that typically require advanced doctoral-level expertise. This proactive approach aims to identify and patch vulnerabilities in the software that might assist an amateur in bypassing standard laboratory safety measures. By simulating potential attack vectors, these red teams provide a realistic assessment of a model’s lethality. This methodology forces developers to consider the physical consequences of their digital outputs, ensuring that safety is integrated into the design phase.
Establishing Actionable Protocols: The Path Forward
To prevent a catastrophic event, the global community established concrete, actionable responses triggered by specific digital and physical indicators. Authorities moved beyond vague agreements and implemented technical safeguards such as mandatory watermarking for biological design systems and more rigorous screening for genetic synthesis providers. These measures allowed for the creation of a transparent trail, enabling security agencies to track whenever individuals attempted to order dangerous genetic sequences via automated laboratories. By strengthening the oversight of these physical gateways, international bodies successfully created a bottleneck that prevented digital designs from being realized in the real world. Legislation to expand this screening provided the necessary legal framework to ensure compliance across the biotechnology industry. Ultimately, the integration of independent testing and government protocols safeguarded the public against AI-driven bioterrorism while allowing for continued medical innovation and biotechnological advancements.